
By Etop Ekanem
Nigerian businesses have been urged to strengthen their cybersecurity frameworks, particularly in digital identity management, vulnerability assessment and incident response, as artificial intelligence makes cyberattacks increasingly sophisticated and difficult to detect.
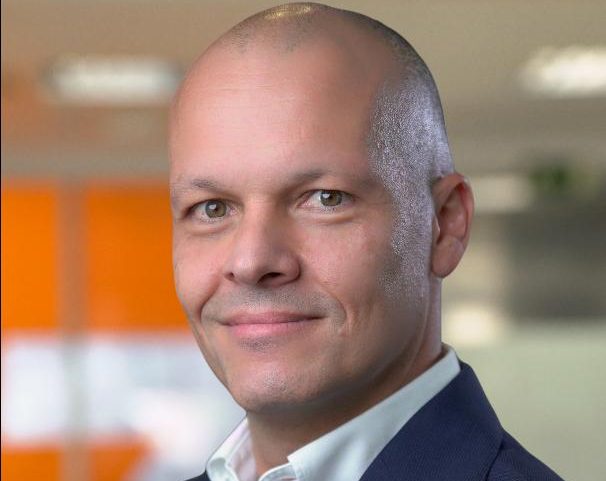
Eric Schifflers, Group Chief Information Security Officer and Head of Governance, Risk and Compliance at TeKnowledge, said Nigeria’s expanding digital economy had created new opportunities for businesses but also exposed organisations to growing cybersecurity risks.
He noted that increased reliance on digital payments, cloud platforms and mobile applications by businesses and public institutions had widened the potential attack surface for cybercriminals.
Speaking during Cybersecurity Awareness Month, Schifflers said artificial intelligence was making cyberattacks more convincing, easier to execute and scalable, increasing the need for organisations to strengthen their defences.
“Organisations not only need to pay close attention to traditional methods of attack such as phishing, but also the human aspects like social engineering, identity and credential theft, and business email compromise,” he said.
“The challenge is not only that threats are becoming more advanced, but that they can also become more successful.”
To improve organisational resilience, Schifflers outlined five priority areas for Nigerian businesses.
First, he advised organisations to identify their critical assets and services, explaining that businesses must understand which systems are most essential to their operations and customers before determining the appropriate security measures.
Second, he emphasised the need to strengthen digital identity management as more services move online. He identified multi-factor authentication and least-privilege access as important measures for ensuring that only authorised individuals can access organisational systems and information.
He also highlighted basic cybersecurity hygiene, urging organisations to regularly review their security programmes and maintain comprehensive inventories of their information technology and operational technology assets.
The fourth priority, he said, is effective vulnerability management and secure configuration. With new security weaknesses emerging regularly, organisations must identify and address vulnerabilities promptly, particularly in systems exposed to the internet.
Finally, businesses must strengthen their capacity to detect, respond to and recover from security incidents.
“The question is no longer whether we are going to suffer a security incident. The question now has focused into when and how quick are we able to detect and also respond to be able to recover as soon as possible from those security incidents,” Schifflers said.
Beyond technical measures, he stressed that cybersecurity should be treated as a business priority rather than the exclusive responsibility of IT departments.
Although cybersecurity specialists may oversee day-to-day security operations, he said organisational leadership must understand the risks and provide appropriate oversight.
“Cybersecurity may be operated and managed on a day-to-day basis by subject matter experts and cybersecurity architects. But the leadership, they must be able to understand to be able to make informed decisions,” he said.
He added that security teams must communicate cyber risks in business terms, highlighting their potential implications for operations, customer confidence, financial performance and regulatory compliance.
Schifflers also called for a stronger cybersecurity culture, describing employees as an important line of defence against cyberattacks.
Rather than relying solely on annual awareness programmes, he advocated continuous, role-specific training that prepares employees to recognise threats relevant to their responsibilities.
For instance, finance teams should be trained to identify payment fraud, while executives need to recognise impersonation attempts and deepfakes. Other employees should also know how to identify and report suspicious communications.
On the growing adoption of artificial intelligence and other emerging technologies, Schifflers cautioned organisations against viewing innovation and security as competing priorities.
“The choice is not between innovation and security. The goal is secure innovation,” he said.
He explained that organisations adopting AI must understand where their data is processed, who has access to it and the potential consequences of technology failures or security breaches.
He identified strong identity management, secure configurations, encryption, continuous monitoring, reliable backups and clear governance structures as essential safeguards for responsible AI adoption.
He added that both employees and organisational leaders must understand their respective responsibilities when deploying and using AI systems.
Schifflers further stressed the importance of collaboration among government, businesses and technology providers in strengthening Nigeria’s cybersecurity ecosystem.
He called for clear regulatory frameworks that protect users while allowing organisations to innovate and adopt emerging technologies securely.
Ultimately, he said, sustaining Nigeria’s digital growth would require organisations to continually adapt their security strategies to evolving technologies and cyber threats.
“Organisations do not have to do this alone. Government and businesses can work with subject-matter experts and technology providers to support the journey,” he said.



No comments yet. Start the conversation.