
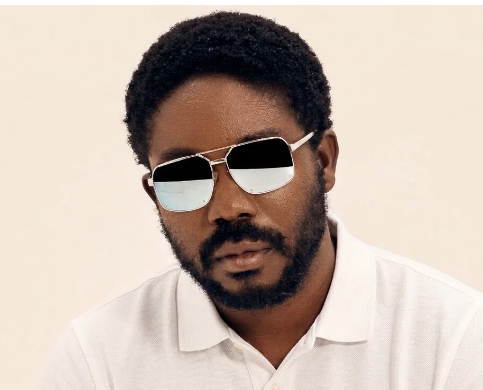
The Founder and Chief Executive Officer of Relm Insurance, Joseph Ziolkowski, speaks with JUSTICE OKAMGBA on the risks autonomous AI systems pose to financial institutions, the potential for technology failures to disrupt interconnected banking systems, and how Nigerian banks and fintech companies can strengthen safeguards against emerging threats
As Nigerian banks and fintech companies increasingly adopt AI for customer service, fraud detection and financial transactions, what potential risks should they assess before granting AI agents autonomy within their systems?
When we look at AI risk anywhere in the world, the first question isn’t whether a company is using AI, because we’re seeing every company globally with some form of AI initiative. The question is the degree to which authority has been delegated to these tools. Are we talking about a company using ChatGPT to draft emails more efficiently, or one using AI agents to transact autonomously?
Wildly different use cases, wildly different exposures. Before an agent operates independently, an institution should be very clear on what it can access, what it can execute and what it can do without human approval, and what permissions, safeguards and human oversight sit around it. You also need to know who owns the outcome, how quickly a person can intervene, and whether you can reconstruct what happened after something goes wrong. Then there’s identity. These agents work across an organisation’s technology and data, which greatly expands the attack surface. A survey of 260 organisations by Okta found just 10 per cent had a well-developed identity management strategy covering both human and agentic identities. Deepfakes are another one. The ability to recreate a CEO’s likeness on a video call means that kind of call is no longer a reliable way to verify an instruction. In a case reported by Hong Kong police in 2024, an employee at the engineering firm Arup authorised transfers totalling $25.6m after a deepfake video call, and no system was breached. Institutions also shouldn’t assume their existing security frameworks cover this. Standards like ISO 27001, the NIST Cybersecurity Framework, and SOC 2 weren’t designed for autonomous decision-making systems.
As Nigeria’s financial system becomes increasingly reliant on digital payments and interconnected banking platforms, what impact could an AI-induced disruption at a major financial institution have on other banks, fintech firms and their customers?
The scale of real-time digital payments in Nigeria is a real strength. The flip side is that when everyone is linked in real time, a problem at one major institution doesn’t stay there. Take a practical example. If a major bank’s AI fraud model is compromised or simply gets it wrong, it can either wave through fraudulent transfers that then move instantly across the network or freeze legitimate accounts at scale. Either way, the fintechs, payment platforms and merchants connected to that bank feel it within minutes, partners may pause connections to protect themselves, and customers experience it as a disruption to services they rely on every day. That’s why third-party risk matters so much. Reporting in Ghana’s Business & Financial Times last year made the point that as embedded finance grows across Africa, it widens the attack surface for cybercriminals, which makes managing third-party risk essential to the integrity of the financial system. The same logic applies to AI. Your exposure includes every provider and partner your AI depends on.
Beyond the existing cybersecurity threats facing banks, why does agentic AI pose a potential systemic threat to the global financial system?
So, the headline-grabbing risk with AI is that it becomes too intelligent, and I think that’s more hyperbole than anything. The real risk is the pace at which companies are deploying AI relative to the governance and controls they’re building around it. Agentic AI makes that gap far more consequential, because these tools aren’t just drafting anymore. They’re being trusted to decide and transact. What takes this beyond the cyber risk banks already manage is where the exposure sits. Traditionally the threat comes from outside, at the network edge. With agentic AI, the exposure moves inward to the point of decision, and these systems act in milliseconds rather than at human speed. The bigger issue from a systemic standpoint is correlation. Banks that compete on everything else increasingly rely on the same three or four foundation-model providers, so their systems can come to behave alike and fail alike. The Financial Stability Board now lists that concentration as one of its key vulnerabilities. The reality is that within financial services, adoption is already moving faster than the market’s understanding of the risks it creates.
According to KPMG, the share of organisations deploying autonomous agents went from 11 per cent to 42 per cent during 2025. Yet research suggests only about a third of firms report mature governance arrangements for those agents. When that gap exists across a whole sector at the same time, it stops being one firm’s problem.
If thousands of AI agents execute financial transactions simultaneously, how could a single system failure cascade across interconnected banks, resulting in widespread financial losses or a liquidity crisis?
When AI agents depend on one another, a defect in one can cascade through the chain and disrupt connected systems and decision flows. Now picture thousands of agents across different banks running on the same handful of models. One flawed update, one manipulated input or one provider outage can hit all of them at the same time. South Africa’s Financial Sector Conduct Authority made this point last year, noting that a problem at any one vendor could cascade across the sector, as the faulty CrowdStrike update showed in 2024. Earlier this year we ran an Emerging Risks Lab with the DIFC Innovation Hub in Dubai, bringing together 23 senior people from banks, regulators, law firms and technology firms. One thing that came through clearly is that a lot of these exposures are shared. As one of the findings put it, everyone is exposed to the same errors, vulnerabilities and outages all at once. That’s not something any single institution can see or manage on its own. The point is that operational problems and financial problems are closer together than people think. If an outage cuts off access to a shared provider, payments and settlement can be disrupted even when every institution involved is perfectly sound. That’s why operational resilience planning has to include your AI dependencies, not just your own systems.
When an AI agent executes an unauthorised transfer or initiates harmful transactions, who should be held financially liable: the bank, AI developer, customer or organisation deploying the technology?
So, the way we look at it as an underwriter is control. The developer, the deploying institution and the end user each sit at different points in the chain, and the question is who had the ability to understand, manage or prevent the harm. That means looking at how the model was designed, how it was implemented, what disclosures were made, and whether the user operated it within the intended parameters. In practice, the chain can involve developers, model providers, deployers, operators and end users, with no single party controlling the whole process. We’re starting to see some early direction. In a Canadian tribunal decision involving Air Canada, the airline was held liable for what its customer service chatbot told a passenger, and the tribunal rejected the argument that the chatbot was a separate legal entity. It’s a small case, but the direction of travel is that a company owns what its AI tells or does for its customers. From the customer’s standpoint, the bank or fintech is the face of the transaction, so that’s where they’ll naturally look first. How the loss is ultimately allocated is a matter for the contracts, the regulator and, if it comes to it, the courts. What I’d say to institutions is get those contracts right before you deploy, because insurance does not fix a bad contract.
How can insurance help Nigerian banks and fintech companies mitigate financial losses arising from autonomous AI systems, and do existing cyber insurance policies sufficiently cover these emerging risks?
Insurance has a remarkable ability to turn existential risks into managed volatility. But is the insurance market fully prepared for all of the new exposures arising from the utilisation of AI? The answer’s no, not yet. Traditional cyber and E&O policies were not necessarily designed around autonomous AI. What concerns me is silent AI. That’s liability arising from the utilisation of AI that the market didn’t see coming, sitting in policies whose wordings don’t clearly address it either way. The market’s reaction has been relatively predictable, which is to start clarifying that through exclusions. In the US, standard exclusion endorsements that took effect in January 2026 allow insurers to remove generative AI claims from conventional liability wordings, and according to CSIS, more than 60 property and casualty insurance groups filed AI exclusions in 2026. So it’s worth checking exactly how your current policies treat AI. The good news is that most of the AI risks we’ve looked at are insurable today. The market is starting to offer affirmative AI cover, and we’ve built some of that at Relm in the markets where we operate. The point for any institution is to have cover that addresses AI explicitly, rather than hoping a traditional policy stretches to fit. My advice to any bank or fintech is to sit down with their broker at renewal and ask a simple question: if our AI agent makes an unauthorised transfer tomorrow, which policy responds?
G Considering the gaps in regulatory capacity, cybersecurity resources and technological infrastructure between Nigeria and more advanced markets, what practical measures can local financial institutions adopt to prepare for the emerging risks associated with agentic AI?
So, the most important steps here are about governance more than technology spending. The biggest risk is deploying AI without the governance that lets you do it in a controlled and deliberate fashion. For starters, map your own exposure before choosing any control or any insurance. Know where AI sits in the business, what authority it has, and what it touches. Then put human-in-the-loop authorisation and audit logging on agentic systems now, because that’s the baseline supervisors will eventually expect to find. The best practice we’re seeing is a multidisciplinary committee overseeing AI projects, bringing in legal, IT security and the teams actually using the technology. And testing needs to be regular, not just a check before deployment. Institutions also need to understand how dependent they are on a relatively small number of AI providers and make sure responsibilities and recovery terms are written clearly into those contracts. On the regulatory side, I think the most useful thing is dialogue. Frameworks everywhere are still catching up with AI, and the markets that handle this well are the ones where supervisors, institutions and insurers compare notes regularly on how agentic systems are actually being used and where the gaps are. The overarching conclusion of the Emerging Risks Lab with the DIFC Innovation Hub was that the industry should become more risk-aware rather than risk-averse. Insurance and good risk management aren’t a brake on innovation. They’re part of the foundation that will enable it to scale.

No comments yet. Start the conversation.